
Merccy's PolyLoader 2.0
PolyLoader
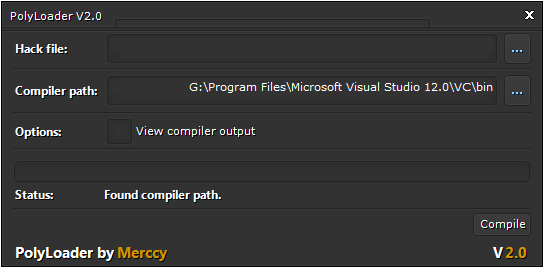
What is PolyLoader?
PolyLoader is a program that opens hack files, randomizes the source code and compiles it.
This process results in an application that is very hard to detect for VAC because the signature changes everytime.
Changelog
View change log
Code:
2.0
---
Better junk code generation
Complete syntax change for hack files
String encryption
New UI
Better performance
Automatic detection of the compiler path
For users
How to use:
1. Download Microsoft Visual Studio Express 2013 for Windows Desktop
2. Download the PolyLoader
3. Download a hack file
4. Open the PolyLoader as admin
5. Select the hack file
6. Press compile
Errors:
"Something went wrong when compiling the randomized source!":
Press the "View compiler output" checkbox and post the data of the console that opens.
Access denied:
Run as admin.
How to use VMProtect/Enigma etc...:
First you have to generate an exe using the loader for instance "PolyHack_RT.exe".
Now you can protect "PolyHack_RT.exe".
Official hack files
Radar & Trigger - Auto updating
RCS - Auto updating
For developers
Everyone can create a hack that supports the PolyLoader platform.
View developer guide
A hack file is just a simple zip with the following files:
-command.txt
-inout.txt
-msg.txt
and a src directory.
So how do I make a hack file?
Step 1, modify your source code.
The PolyLoader uses a few tags to understand your file:
[swap_lines][/swap_lines] - Swap the lines between the 2 tags, useful for randomizing a structure.
[junk_enable /] - Enables auto junk code addition, the PolyLoader will add junk code after every ;
You can give it 1 or 2 parameters
[junk_enable 5 /] - Will add 5 lines of junk code after every ;
[junk_enable 5 10 /] - Will add 5 to 10 lines of junk code after every;
[junk_disable /] - Disables auto junk code addition.
[junk_enable_declares /] - The auto junk code generator will now only make declares (useful for in header files).
[add_junk /] - Adds a block of junk code at this position, it does NOT take junk_enable_declares into account.
[swap_blocks][/swap_blocks] - Works like swap_lines but instead it swaps blocks of code.
[block][/block] - Define a block
[enc_string_enable /] - Scrambles all strings, when you are using this make sure you have Decrypt.h included (the loader will generate a randomized Decrypt.h file).
[enc_string_disable /] - Disables the auto string scrambler.
command.txt
In command.txt you have to fill in the command line compiler options, here you have to link all the libraries etc... this one should work for practically any hack.
inout.txt
First line you put the filename the compiler generates (see the /OUT: parameter)
Second line the new name.
msg.txt
A message that will pops up when the user loads up the hack.
If you have any question regarding implementing this system sent me a pm .
-command.txt
-inout.txt
-msg.txt
and a src directory.
So how do I make a hack file?
Step 1, modify your source code.
The PolyLoader uses a few tags to understand your file:
[swap_lines][/swap_lines] - Swap the lines between the 2 tags, useful for randomizing a structure.
Code:
struct Entity {
	[swap_lines]
	DWORD dwBase;
	int id;
	int hp;
	int team;
	int weapon_id;
	int weapon_ammo;
	[/swap_lines]
};
You can give it 1 or 2 parameters
[junk_enable 5 /] - Will add 5 lines of junk code after every ;
[junk_enable 5 10 /] - Will add 5 to 10 lines of junk code after every;
[junk_disable /] - Disables auto junk code addition.
[junk_enable_declares /] - The auto junk code generator will now only make declares (useful for in header files).
[add_junk /] - Adds a block of junk code at this position, it does NOT take junk_enable_declares into account.
[swap_blocks][/swap_blocks] - Works like swap_lines but instead it swaps blocks of code.
[block][/block] - Define a block
Code:
[swap_blocks]
[block]
if (x == 5) {
    std::cout << "x == 5\n";
}
[/block]
[block]
if (y == 7) {
    std::cout << "y == 7\n";
}
[/block]
[/swap_blocks]
[enc_string_disable /] - Disables the auto string scrambler.
command.txt
In command.txt you have to fill in the command line compiler options, here you have to link all the libraries etc... this one should work for practically any hack.
Code:
/EHsc /Od /MT *.cpp kernel32.lib user32.lib gdi32.lib winspool.lib comdlg32.lib advapi32.lib shell32.lib ole32.lib oleaut32.lib uuid.lib /link /FORCE:MULTIPLE /OUT:hack.exe
First line you put the filename the compiler generates (see the /OUT: parameter)
Second line the new name.
Code:
hack.exe
MyHack.exe
A message that will pops up when the user loads up the hack.
If you have any question regarding implementing this system sent me a pm
.Download
Virusscan - Jotti
Virusscan - Virustotal
Credits
@Sandwich - The icon

 Originally Posted by fofoktb


