Hooking DeviceIoControl.

Posts 1–13 of 13 · Page 1 of 1
Hooking DeviceIoControl.
Hello mpgh!

Recently I got a HWID ban in CFRU and trying to bypass it for a few days.
I tried to change all the IDs that I could, but in the end nothing helped me, so I decided to hook the DeviceIoControl (This is my first experience with writing a hook, so the code can be bad, please correct me)

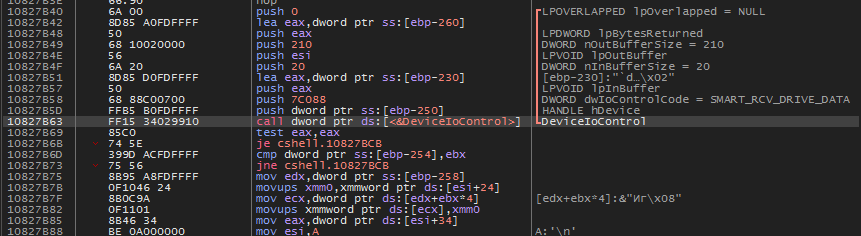
I attached debugger to LoadLibrary and found the DeviceIoControl function in kernelbase.dll


I saw 3 calls from cshell.dll and chose them to hook (idk why now is kernel32.dll)
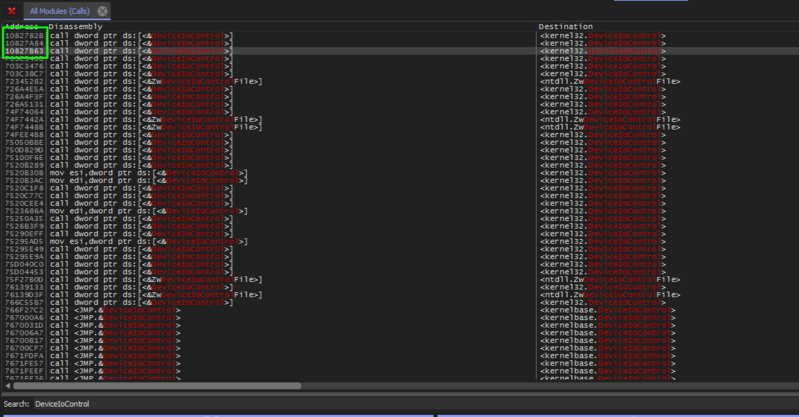


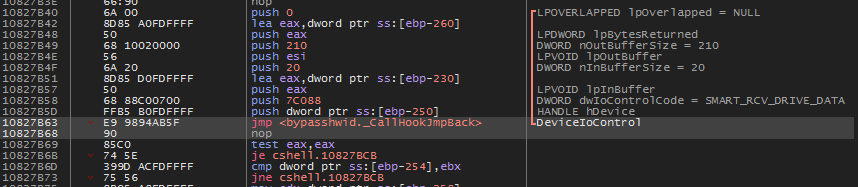
My code:
Code:
// C language
#include <windows.h>
#include <stdbool.h>

#define CALL1_OFFSET 0xFA782B
#define CALL2_OFFSET 0xFA7A84
#define CALL3_OFFSET 0xFA7B63

//Global variables
DWORD HookAddr = 0;
DWORD JmpBackAddr = 0;

//Call the hook function and jump back to next instruction
void __declspec(naked) CallHookJmpBack() {
    __asm {
        call [HookAddr]; //call the hook func
        jmp [JmpBackAddr]; //jump back
    }
}

//Prototypes
bool Hook(void* toHook, void* asmFunc, int len);

//Hack
DWORD WINAPI init(HMODULE hModule) {
    DWORD cshell = (DWORD)GetModuleHandle("cshell.dll");
    if (cshell)  {
        DWORD callAddr = 0;

        //Hooking calls
        callAddr = (DWORD)(cshell + CALL1_OFFSET);
        Hook((void*)callAddr, CallHookJmpBack, 6);
        
        callAddr = (DWORD)(cshell + CALL2_OFFSET);
        Hook((void*)callAddr, CallHookJmpBack, 6);

        callAddr = (DWORD)(cshell + CALL3_OFFSET);
        Hook((void*)callAddr, CallHookJmpBack, 6);

       
        MessageBox(0, "Hooked", "Success", MB_OK);
    }

    while (0x01) {
        if (GetAsyncKeyState(VK_INSERT) & 1)
            break;
    }

    FreeLibraryAndExitThread(hModule, 0);
}

//The function to replace the main one with
BOOL hookDeviceIoControl(
    HANDLE       hDevice,
    DWORD        dwIoControlCode,
    LPVOID       lpInBuffer,
    DWORD        nInBufferSize,
    LPVOID       lpOutBuffer,
    DWORD        nOutBufferSize,
    LPDWORD      lpBytesReturned,
    LPOVERLAPPED lpOverlapped
)
{
    // I just call the main function to change the received data after
    bool DIC = DeviceIoControl(hDevice, dwIoControlCode, lpInBuffer, nInBufferSize, lpOutBuffer, nOutBufferSize, lpBytesReturned, lpOverlapped);
    
    // [Return fake data]
    // Now i don't do anything because i just want to check if everything is OK

    return DIC;
}

bool Hook(void* toHook, void* asmFunc, int len) {
    if (len < 5)
        return FALSE;

    //Store the address of DIC hook function
    HookAddr = (DWORD)hookDeviceIoControl;
    //Store the address of the next instruction to jmp back
    JmpBackAddr = (DWORD)toHook + len;

    //Change the protection
    DWORD oldProtect = 0;
    VirtualProtect(toHook, len, PAGE_EXECUTE_READWRITE, &oldProtect);

    //Fill with NOP
    memset(toHook, 0x90, len);

    //Relative address
    DWORD targetAddr = ((DWORD)asmFunc - (DWORD)toHook) - 5;

    //Change first byte to jmp
    *(BYTE*)toHook = 0xE9;
    //Jump to relative address
    *(DWORD*)((DWORD)toHook + 1) = targetAddr;

    //Restore protection
    DWORD tempProtect = 0;
    VirtualProtect(toHook, len, oldProtect, &tempProtect);

    return TRUE;
}


BOOL __stdcall DllMain(HMODULE hModule, DWORD dwReason, LPVOID lpReserved) {
    if (dwReason == DLL_PROCESS_ATTACH) {
        CreateThread(0, 0, (LPTHREAD_START_ROUTINE)init, hModule, 0, 0);
    }

    return TRUE;    
}

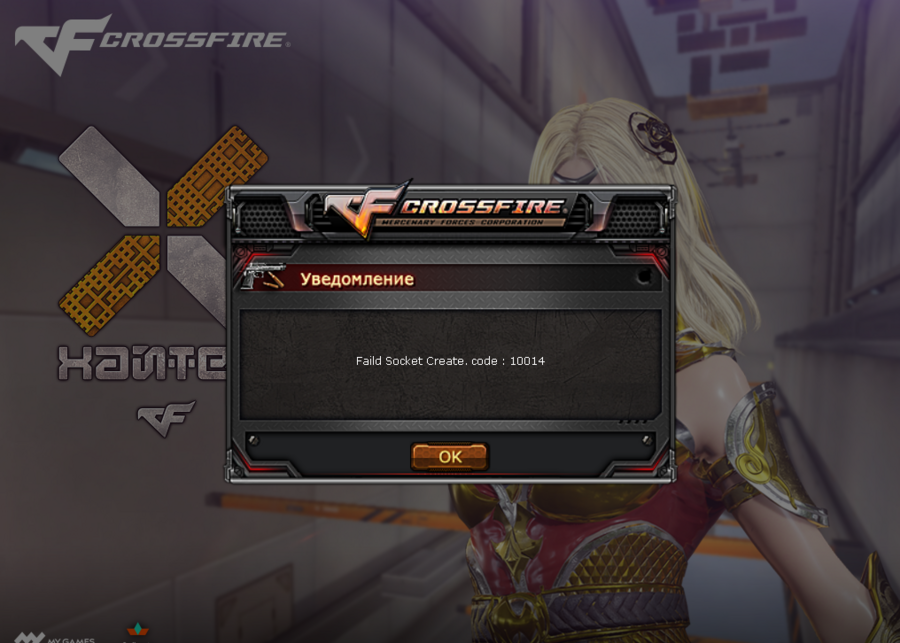
I injected this dll to LoadLibrary. No crashes, good.


What can not be said about the crossfire.


I've experimented a lot with code and addresses, but without results.
Please tell me where my mistake is. Thanks ^^
you can hook directly to the ntdll so you don't miss anything -> NtDeviceIoControlFile(google it to know the parameters)

on cfbr they are checking hook on kernel32.dll, ntdll.dll and other modules, I don't know if in this version they are checking, so it would be better to unhook after spoofing the data


you can use minhook, it would be the best option
Quote Originally Posted by Joaoemariana View Post
you can hook directly to the ntdll so you don't miss anything -> NtDeviceIoControlFile(google it to know the parameters)

on cfbr they are checking hook on kernel32.dll, ntdll.dll and other modules, I don't know if in this version they are checking, so it would be better to unhook after spoofing the data


you can use minhook, it would be the best option
So i hooked ZwDeviceIoControlFile successfully
Code:
typedef NTSTATUS(WINAPI* pZwDeviceIoControl)(HANDLE FileHandle, HANDLE Event, PIO_APC_ROUTINE ApcRoutine, PVOID ApcContext, PIO_STATUS_BLOCK IoStatusBlock, ULONG IoControlCode, PVOID InputBuffer, ULONG InputBufferLength, PVOID OutputBuffer, ULONG OutputBufferLength);
pZwDeviceIoControl fpZwDeviceIoControl = 0;

NTSTATUS ProxyZwDeviceIoControlFile(
    HANDLE           FileHandle,
    HANDLE           Event,
    PIO_APC_ROUTINE  ApcRoutine,
    PVOID            ApcContext,
    PIO_STATUS_BLOCK IoStatusBlock,
    ULONG            IoControlCode,
    PVOID            InputBuffer,
    ULONG            InputBufferLength,
    PVOID            OutputBuffer,
    ULONG            OutputBufferLength
)
{
    return	(fpZwDeviceIoControl(FileHandle, Event, ApcRoutine, ApcContext, IoStatusBlock, IoControlCode, InputBuffer, InputBufferLength, OutputBuffer, OutputBufferLength));
}
but now, idk why, i'm getting a socket related error


...


I'll just give up, thanks for your answer.
you must spoof your machine information inside the hook, there are several examples on the internet of how to do this

simple spoofer hd

Code:
if(IoControlCode == IOCTL_STORAGE_QUERY_PROPERTY)
{
PSTORAGE_PROPERTY_QUERY Query = PSTORAGE_PROPERTY_QUERY( InputBuffer );
				if ( Query && Query->PropertyId == StorageDeviceProperty )
				{
					if ( OutputBufferLength >= sizeof( STORAGE_DEVICE_DESCRIPTOR ) )
					{
						PSTORAGE_DEVICE_DESCRIPTOR Desc = PSTORAGE_DEVICE_DESCRIPTOR( OutputBuffer );
						if ( Desc )
						{
							if ( Desc->SerialNumberOffset )
							{
								auto Serial = PCHAR( Desc ) + Desc->SerialNumberOffset;								
								memset( Serial, 0, strlen( Serial ) );
								strcpy( Serial, "ABCDEFG" );
							}

							if ( Desc->ProductIdOffset )
							{
								auto Model = PCHAR( Desc ) + Desc->ProductIdOffset;								
								memset( Model, 0, strlen( Model ) );
								strcpy( Model, "ABCDEFG" );
							}
						}
					}
				}
}
or you can just return a STATUS_UNSUCCESSFUL and see what happens
Quote Originally Posted by Joaoemariana View Post
you must spoof your machine information inside the hook, there are several examples on the internet of how to do this

simple spoofer hd

Code:
if(IoControlCode == IOCTL_STORAGE_QUERY_PROPERTY)
{
PSTORAGE_PROPERTY_QUERY Query = PSTORAGE_PROPERTY_QUERY( InputBuffer );
				if ( Query && Query->PropertyId == StorageDeviceProperty )
				{
					if ( OutputBufferLength >= sizeof( STORAGE_DEVICE_DESCRIPTOR ) )
					{
						PSTORAGE_DEVICE_DESCRIPTOR Desc = PSTORAGE_DEVICE_DESCRIPTOR( OutputBuffer );
						if ( Desc )
						{
							if ( Desc->SerialNumberOffset )
							{
								auto Serial = PCHAR( Desc ) + Desc->SerialNumberOffset;								
								memset( Serial, 0, strlen( Serial ) );
								strcpy( Serial, "ABCDEFG" );
							}

							if ( Desc->ProductIdOffset )
							{
								auto Model = PCHAR( Desc ) + Desc->ProductIdOffset;								
								memset( Model, 0, strlen( Model ) );
								strcpy( Model, "ABCDEFG" );
							}
						}
					}
				}
}
or you can just return a STATUS_UNSUCCESSFUL and see what happens
Yes, but first i want to check if hook is correctly coded by emulating the work of the original function without changing anything. At this step i have problems. Anyway thanks
Quote Originally Posted by 0x171 View Post
Yes, but first i want to check if hook is correctly coded by emulating the work of the original function without changing anything. At this step i have problems. Anyway thanks
if the hook is not correct your game will crash
Quote Originally Posted by Joaoemariana View Post
if the hook is not correct your game will crash
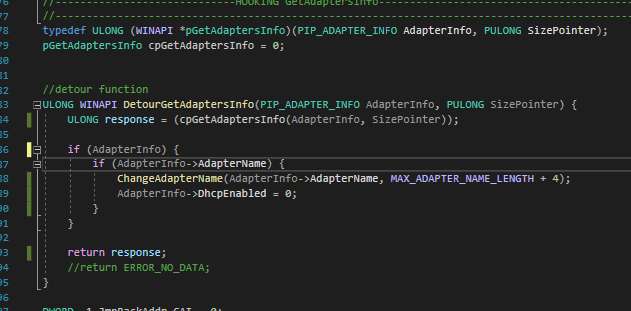
Finally I wrote correctly my hook of DeviceIoControlFile and returned STATUS_UNSUCCESSFUL without any errors, but anyway got banned. I will try to hook also GetVolumeInformation and GetAdaptersInfo, maybe it will work. Thank you so much for your help!
Quote Originally Posted by 0x171 View Post
Finally I wrote correctly my hook of DeviceIoControlFile and returned STATUS_UNSUCCESSFUL without any errors, but anyway got banned. I will try to hook also GetVolumeInformation and GetAdaptersInfo, maybe it will work. Thank you so much for your help!
use some spoofer kernel to spoof all your machine information and see if it will still be banned, if you continue to be banned it can be verified by wifi modem ip, many ant-cheats are doing this
can you try ?

Code:
ULONG WINAPI GetAdaptersInfoHook(PIP_ADAPTER_INFO AdapterInfo, PULONG SizePointer)
{
	auto res = STDCALL_T(DWORD, oGetAdaptersInfo, 2, AdapterInfo, SizePointer);
	if (res == 0)
	{
		PIP_ADAPTER_INFO pAdapter = AdapterInfo;
		if (pAdapter)
		{
			while (pAdapter)
			{
				for (UINT i = 0; i < pAdapter->AddressLength; i++)
					pAdapter->Address[i] = 0xFF;

				pAdapter = pAdapter->Next;
			}
		}
	}
	return res;
}
Quote Originally Posted by jayjay153 View Post
can you try ?

Code:
ULONG WINAPI GetAdaptersInfoHook(PIP_ADAPTER_INFO AdapterInfo, PULONG SizePointer)
{
	auto res = STDCALL_T(DWORD, oGetAdaptersInfo, 2, AdapterInfo, SizePointer);
	if (res == 0)
	{
		PIP_ADAPTER_INFO pAdapter = AdapterInfo;
		if (pAdapter)
		{
			while (pAdapter)
			{
				for (UINT i = 0; i < pAdapter->AddressLength; i++)
					pAdapter->Address[i] = 0xFF;

				pAdapter = pAdapter->Next;
			}
		}
	}
	return res;
}
Thx, i will try

I already tested this


And also hooked NtQueryVolumeInformationFile, ZwDeviceIoControlFile and returned STATUS_UNSUCCESSFUL.

No results.
Quote Originally Posted by 0x171 View Post
Thx, i will try

I already tested this


And also hooked NtQueryVolumeInformationFile, ZwDeviceIoControlFile and returned STATUS_UNSUCCESSFUL.

No results.
did you try to change the Address ?
Quote Originally Posted by jayjay153 View Post


did you try to change the Address ?
Yes, but it didn't help.
never give up, my friend
никогда не сдавайся, друг мой
Posts 1–13 of 13 · Page 1 of 1

Post a Reply

Similar Threads

Tags for this Thread

None

Talk with us