Another New Private Server!

Posts 31–45 of 92 · Page 3 of 7
Quote Originally Posted by Durdan View Post


Like who? Do you have proof? Are you sure they didn't hack or had any past offenses?
If you are on the cf groups on fb then no need to post proof.
Some got deleted already
Quote Originally Posted by Jonathan View Post
If you are on the cf groups on fb then no need to post proof.
Some got deleted already
Yes, I'm such a die hard fan of CF that I've joined all CF groups out there >.>
Quote Originally Posted by Durdan View Post


Yes, I'm such a die hard fan of CF that I've joined all CF groups out there >.>
Who created the private server?
Quote Originally Posted by Durdan View Post


Yes, I'm such a die hard fan of CF that I've joined all CF groups out there >.>
There's like 2-3.. LOL
Quote Originally Posted by ImMalkah View Post


Who created the private server?
Only Dev's show who they are, I personally don't know who the owner is. All I know is his name is ARXGaming on the forum xD


- - - Updated - - -

Quote Originally Posted by Jonathan View Post
There's like 2-3.. LOL
It doesn't matter, I don't want to join a CF group seems... foolish like the word: 'Hashtag'
BlazeCF will be released in a few days also!
Quote Originally Posted by kiridmode View Post
BlazeCF will be released in a few days also!
da fuq is BlazeCF?

Dammit it's fucking a BR ps....
Any clearance on the KeyLogger? Where is it in the folder? I'm scanning right now, too much to be lost.
Quote Originally Posted by Killspo View Post
Any clearance on the KeyLogger? Where is it in the folder? I'm scanning right now, too much to be lost.
Keylogger confirmed. Check your %temp% folder .
Quote Originally Posted by ImMalkah View Post


Keylogger confirmed. Check your %temp% folder .
to remove it you just empty you %temp% folder right? and does the key logger end in .xx?
Attention everyone: I come to confirm there is a keylogger in this private server mod. Below, I will explain briefly what the virus is, and how to remove it, as it is very difficult.

What is the virus?

It's a keylogger/backdoor that goes by the name of "Ratenjay". Ratenjay backdoors are one of the most dangerous keyloggers out there due to the recent growth of it. It's very hard to remove. "But Spank, I have an anti-virus and I can just remove it from there.." < false; it will give you blue screen and crash your computer. "I can just download a file shredder" < false; file shredders can only shred files that are not in memory, AKA not running. This virus is always a hidden process you can't see in task manager. "I found the process, I can just end it" < false; the executable denies all permissions of the user. Only the system can access it, and it is controlling the system. Therefore, it can only access/end itself when it wants, which it will not.

Note: backdoor.ratenjay isn't the same as backdoor.ratenjay.b; don't get those confused.

Where can I locate it?

The sneaky thing about ratenjay is it conceals itself as a normal program on your computer. For example, the keylogger detected I have Google Chrome installed on my computer, therefore, it disguised the executable as "google chrome.exe". Also, it's really difficult to locate the keylogger as it contains a location and name randomizer. Basically unlike most other viruses, this one you cannot locate, it's not a fixed location common for everyone. Your best bet is to check your %temp%, that's where I found mine. (delete all the files in there, there will be some files that cannot be deleted, press okay and run a scan on all the files that aren't able to be deleted. If your anti-virus says files are clean, it's not in your temp folder.)

How do I delete it?

After hours upon hours of trying new methods, downloading file shredders and force file deleters, I finally found a solution that works for me. Earlier I said that if you try to remove the keylogger in your anti-virus, you will get a blue screen, aka crash. So check this out:

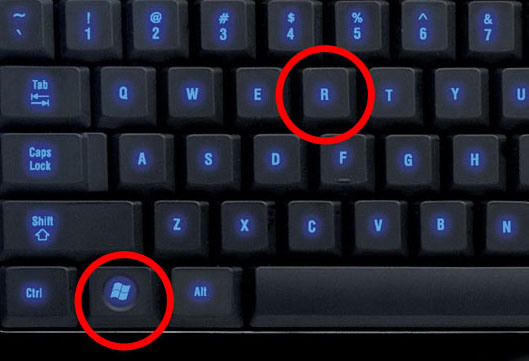
Step 1: Start up "Run" by holding the Windows Key + R


Step 2: Type in "msconfig" and press enter


Step 3: Select "Selective startup" and uncheck both "Load system services" and "Load startup items"; hit apply, ok, then when you get prompted to restart system, do it


Step 4: Once system is restarted, start up your anti-virus, run a full system scan, and remove all detected files

Step 5: That's it, you're done.

Please do not proceed to download this. Do it at your own risk, I have warned you. If you really want to play this, I'd recommend downloading VMware, contacting @JohnnyAWP for a bypass, then downloading this version of CF on there. (It's really not worth the trouble, do not waste your money, it will just get shutdown eventually after a while like the other 2 private servers, it's fun to spend the 1 million ZP though.)


Hope this helped, again, I would not recommend downloading. Do it at your own risk.


- - - Updated - - -

Quote Originally Posted by Mr.Carter View Post
to remove it you just empty you %temp% folder right? and does the key logger end in .xx?
Note exactly, look here for how to remove in case you missed it .
Quote Originally Posted by ImMalkah View Post
Attention everyone: I come to confirm there is a keylogger in this private server mod. Below, I will explain briefly what the virus is, and how to remove it, as it is very difficult.

What is the virus?

It's a keylogger/backdoor that goes by the name of "Ratenjay". Ratenjay backdoors are one of the most dangerous keyloggers out there due to the recent growth of it. It's very hard to remove. "But Spank, I have an anti-virus and I can just remove it from there.." < false; it will give you blue screen and crash your computer. "I can just download a file shredder" < false; file shredders can only shred files that are not in memory, AKA not running. This virus is always a hidden process you can't see in task manager. "I found the process, I can just end it" < false; the executable denies all permissions of the user. Only the system can access it, and it is controlling the system. Therefore, it can only access/end itself when it wants, which it will not.

Note: backdoor.ratenjay isn't the same as backdoor.ratenjay.b; don't get those confused.

Where can I locate it?

The sneaky thing about ratenjay is it conceals itself as a normal program on your computer. For example, the keylogger detected I have Google Chrome installed on my computer, therefore, it disguised the executable as "google chrome.exe". Also, it's really difficult to locate the keylogger as it contains a location and name randomizer. Basically unlike most other viruses, this one you cannot locate, it's not a fixed location common for everyone. Your best bet is to check your %temp%, that's where I found mine. (delete all the files in there, there will be some files that cannot be deleted, press okay and run a scan on all the files that aren't able to be deleted. If your anti-virus says files are clean, it's not in your temp folder.)

How do I delete it?

After hours upon hours of trying new methods, downloading file shredders and force file deleters, I finally found a solution that works for me. Earlier I said that if you try to remove the keylogger in your anti-virus, you will get a blue screen, aka crash. So check this out:

Step 1: Start up "Run" by holding the Windows Key + R


Step 2: Type in "msconfig" and press enter


Step 3: Select "Selective startup" and uncheck both "Load system services" and "Load startup items"; hit apply, ok, then when you get prompted to restart system, do it


Step 4: Once system is restarted, start up your anti-virus, run a full system scan, and remove all detected files

Step 5: That's it, you're done.

Please do not proceed to download this. Do it at your own risk, I have warned you. If you really want to play this, I'd recommend downloading VMware, contacting @JohnnyAWP for a bypass, then downloading this version of CF on there. (It's really not worth the trouble, do not waste your money, it will just get shutdown eventually after a while like the other 2 private servers, it's fun to spend the 1 million ZP though.)


Hope this helped, again, I would not recommend downloading. Do it at your own risk.


- - - Updated - - -


Note exactly, look here for how to remove in case you missed it .
when i remove it can i still run the game or will it reinstall when opening the launcher
Quote Originally Posted by Jonathan View Post
Omgosh I was gonna go to bed and then come to this^ ;_;
Ugh. Time to stay up I guess LOL
Hahahaha

Cleaning your computer > sleeping .


- - - Updated - - -

Quote Originally Posted by Mr.Carter View Post
when i remove it can i still run the game or will it reinstall when opening the launcher
no LOL you start by deleting the game
Quote Originally Posted by ImMalkah View Post


Hahahaha

Cleaning your computer > sleeping .
Bruh I don't need to clean my comp cause I don't fall for these scams LOL
But I do need to FIX my comp...
Omgosh I was gonna go to bed and then come to this^ ;_;
Ugh. Time to stay up I guess LOL

Edit:
Nice tutorial on how to remove the keylogger.
Good thing I never downloaded it, haha.

As for the VMWare bypass, I may not be able to work on that for a few days.
My computer decided to auto update to Windows8.1 and all softwares stopped working.
Since it's my birthday today (18th, in case it's still the 17th for some people), I'll just work on this tomorrow and stuff.


Good luck removing the keylogger, everyone !
Posts 31–45 of 92 · Page 3 of 7
This thread is closed for replies.

Similar Threads

Tags for this Thread

None

Talk with us